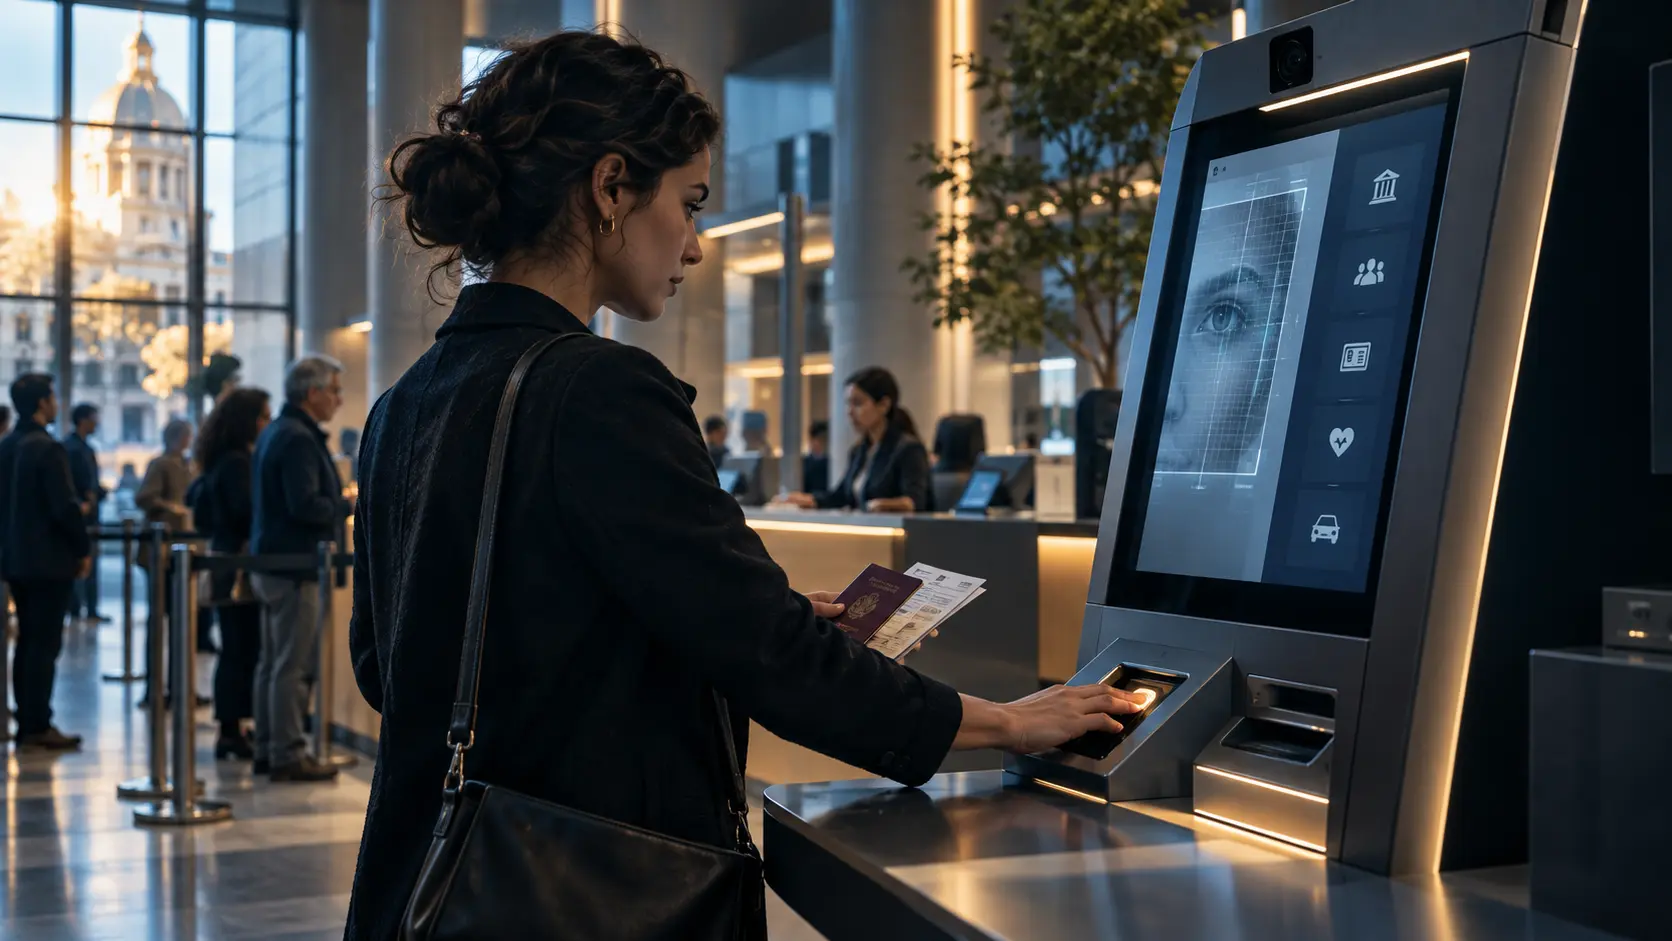
Digital identity is a system that allows a person to prove who they are through electronic means. Governments increasingly use digital identity to give citizens access to public services without requiring repeated in-person visits, paper documents, or separate registration procedures for every agency. A digital identity may combine usernames, passwords, cryptographic credentials, identity databases, mobile applications, biometric verification, and official records. As public administration becomes more digital, these systems can make government services faster and easier to use, but they can also become critical infrastructure whose failures affect people's ability to exercise basic rights.
Traditional identity systems depend heavily on physical documents. Birth certificates, identity cards, driver's licenses, passports, and other credentials establish legal identity in different situations. Citizens often need to present these documents repeatedly when applying for benefits, registering property, filing taxes, enrolling in services, or dealing with government agencies.
Digital identity attempts to move some of this process into electronic systems. Instead of proving identity from the beginning every time, a citizen may establish a verified digital credential that can be accepted by multiple public services. A secure login can then connect the person to information already held in government records.
Authentication is one of the central functions of digital identity. Identification answers the question of who a person is, while authentication confirms that the person attempting to access a service is actually the individual associated with a particular identity. These processes are related but not identical.
A government may establish a person's identity by checking official records and documents. Once that identity is verified, the person may create digital authentication credentials. Those credentials can include a password, a security key, a code sent to a registered device, an authentication application, a digital certificate, or a biometric factor.
Multi-factor authentication combines more than one method. A citizen might need both a password and a temporary code generated on a phone. The goal is to make unauthorized access more difficult because stealing one credential is not sufficient to enter the account.
Biometrics can also become part of digital identity systems. Facial verification, fingerprints, or other physical characteristics may be used to establish or confirm identity. A person registering remotely could take a photograph and have it compared with an official identity document. Biometric authentication can make some processes easier, but it introduces privacy, accuracy, and security concerns because biometric traits cannot be changed as easily as passwords.
Digital credentials can take several forms. Some systems rely on a central government account that citizens use across agencies. Others provide electronic identity cards or certificates. Mobile identity applications can store credentials on smartphones, while newer approaches may allow people to prove particular facts about themselves without revealing every piece of information contained in an identity record.
For example, a service may need to know that someone is above a certain age without needing the person's complete date of birth or home address. A carefully designed digital credential can potentially confirm the necessary attribute while limiting unnecessary disclosure. This principle is related to data minimization: collecting or sharing only the information needed for a particular purpose.
The practical attraction of digital identity is easy to understand. Public administration often forces citizens to repeat the same steps because government agencies maintain separate databases and procedures. A person may submit the same name, address, birth date, and identification documents to several departments.
Integrated digital identity can reduce this duplication. Once a person's identity is reliably established, authorized services can use the same authentication infrastructure. A citizen may be able to file taxes, request certificates, manage social benefits, access healthcare portals, sign official documents, or communicate with agencies from one verified account.
This can be especially valuable for people who live far from administrative offices, have limited mobility, or need to complete procedures outside normal working hours. Digital services can remain available continuously and reduce travel, waiting times, and paperwork.
Governments can also benefit from more reliable identity management. Strong authentication can reduce some forms of impersonation and fraud. Integrated records may help agencies avoid duplicate registrations, identify administrative errors, and deliver services more efficiently.
Digital identity can support electronic signatures as well. When a digital credential is linked to a legally recognized signing mechanism, citizens may be able to complete transactions that previously required paper forms or physical presence. Businesses can similarly interact with government agencies more efficiently.
However, convenience can create dependence. If digital identity becomes the primary gateway to public administration, losing access to an account can become much more serious than forgetting a password to an ordinary website. A person may suddenly be unable to access benefits, tax records, health information, licenses, or other essential services.
Account recovery is therefore a central design issue. Systems need secure ways to help users who lose a phone, forget credentials, change contact information, or become victims of identity theft. Recovery procedures must be accessible enough to prevent permanent exclusion while remaining strong enough to prevent attackers from taking control of accounts.
Errors in government records create another risk. A misspelled name, incorrect birth date, outdated address, duplicated record, or mistaken identity link can prevent successful authentication. When many services depend on the same identity infrastructure, a single database error can affect multiple areas of a person's life.
Citizens need clear procedures for correcting such mistakes. A digital identity system becomes difficult to challenge if agencies simply assume that central records are accurate. Effective systems provide ways to review information, submit evidence, correct errors, and escalate cases that automated processes cannot resolve.
Centralization raises additional concerns. A centralized identity system can make administration simpler because agencies rely on one authoritative source. At the same time, concentrating identity information can create security and privacy risks. A breach affecting a central database may expose sensitive information about very large numbers of people.
Central systems can also make it easier to link records across agencies. Integration can improve services, but it can also increase the government's ability to build detailed profiles of individuals. Information originally collected for taxation, healthcare, education, or transportation may become easier to combine.
This creates the risk of function creep. A digital identity program introduced to simplify access to services can gradually expand into unrelated forms of monitoring or control. Preventing this requires legal and technical restrictions defining which agencies may access particular information and for what purposes.
Good system design can reduce unnecessary data sharing. A digital identity platform does not always need to reveal the full underlying record to every service. It may simply confirm that authentication succeeded or that a required attribute has been verified. Limiting data exchange reduces the amount of sensitive information exposed during routine transactions.
Privacy also depends on whether the identity system records where and when people use it. A centralized authentication service may technically be able to observe interactions across multiple government services. Logging may be necessary for security, fraud investigation, and troubleshooting, but excessive retention can create detailed records of citizens' activities.
Security must therefore be built into digital identity from the beginning. Encryption, access controls, secure authentication methods, monitoring, vulnerability testing, and careful management of administrative privileges are all important. A digital identity system is an attractive target because compromising it can provide access to many services at once.
The involvement of private technology companies can complicate these issues. Governments may rely on contractors for cloud infrastructure, authentication software, biometric verification, or cybersecurity. Contracts need to specify who controls identity data, whether vendors may reuse information, how breaches are handled, and what happens when a contract ends.
Vendor dependence can become a strategic concern if public services are built around proprietary infrastructure that is difficult to replace. Identity systems may operate for decades, so governments need to consider interoperability, long-term maintenance, and the ability to migrate to different technology providers.
Digital exclusion is another major challenge. Not everyone owns a modern smartphone, has reliable internet access, possesses strong digital skills, or can easily use biometric systems. Older people, people with disabilities, low-income communities, rural populations, migrants, and others may encounter particular obstacles depending on how the system is designed.
A digital-first government should therefore not automatically become a digital-only government. Alternative access methods remain important, especially for essential services. Citizens may need assistance through physical offices, telephone services, authorized representatives, or other channels.
Accessibility should also be considered during design rather than added later. Interfaces need to work with assistive technologies, avoid unnecessary complexity, and provide clear instructions. Authentication methods that rely heavily on smartphones or particular physical abilities can exclude users unless alternatives are available.
Biometric identity systems require special caution because people may fail verification for reasons beyond their control. Lighting, camera quality, changes in appearance, disabilities, injuries, age, or technical errors can affect performance. A failed facial match should not automatically mean that a legitimate citizen loses access to essential services.
Human support is therefore important even in highly automated identity systems. Staff need the authority to investigate exceptional cases, correct records, verify alternative evidence, and restore access when automated processes fail. Human review should function as a genuine remedy rather than an inaccessible last resort.
Digital identity can also influence the relationship between individuals and private businesses. Governments may allow official digital credentials to be used for banking, age verification, travel, telecommunications, or other regulated services. This can make identity checks easier but expands the importance of the underlying infrastructure.
The more widely a digital identity is accepted, the more damaging exclusion or compromise becomes. A single credential can become a gateway to both public and private life. Strong governance is therefore as important as technical security.
Some digital identity approaches attempt to give users greater control over their credentials. Instead of every organization contacting a central database whenever identity must be proven, citizens may hold digitally signed credentials that can be verified independently. This can reduce unnecessary central tracking, although such systems introduce their own technical and governance challenges.
Interoperability is another important consideration. Citizens may need to use digital identity across different levels of government or even across national borders. Common standards can make this possible, but shared standards also require agreement about security, privacy, liability, and recognition of credentials.
Digital identity systems also need clear rules about people whose circumstances change. Names change, citizenship status can change, addresses change, documents expire, and legal guardianship relationships may be created or terminated. Identity infrastructure must handle these events without forcing users into complicated administrative processes.
Children and dependent adults require additional consideration because they may not be able to manage credentials independently. Systems need mechanisms for parents, guardians, caregivers, or legal representatives while preventing unauthorized access.
Another challenge involves people who lack complete documentation. A digital identity program can make services more accessible for established citizens while unintentionally making them harder to obtain for people whose records are missing, inconsistent, or historically incomplete. Governments must decide how individuals can enter the system when the documents normally used for verification are unavailable.
This illustrates why digital identity is not merely an information technology project. It defines how institutions recognize people. Decisions about which documents count, which databases are authoritative, which errors are acceptable, and which alternatives exist can determine whether someone is able to access government at all.
Transparency can improve trust. Citizens should be able to understand which information the system stores, how authentication works, which agencies can access data, how activity logs are used, and what happens after a security incident. Privacy policies alone are not enough if they are too technical for ordinary users.
Independent oversight may also be necessary, especially when digital identity becomes national infrastructure. Data-protection authorities, auditors, legislatures, courts, and cybersecurity bodies can examine whether the system complies with legal requirements and whether its powers are expanding beyond the purposes originally authorized.
Digital identity offers substantial benefits when it reduces unnecessary bureaucracy without creating new barriers. A well-designed system can allow citizens to prove who they are once and then interact with public institutions more easily, securely, and consistently. It can save time for both citizens and government employees while reducing some opportunities for fraud.
The risks become more serious when access depends on a single system that is difficult to correct, difficult to leave, or impossible to use without specific technology. Centralized identity can simplify administration while also concentrating sensitive information and institutional power.
As government services continue moving online, digital identity is becoming more than a convenient login mechanism. It can become essential infrastructure for accessing documents, benefits, healthcare, taxes, education, and other rights. That makes reliability, privacy, accessibility, security, and the ability to challenge errors fundamental requirements rather than optional features. A digital identity system succeeds not merely when it verifies people efficiently, but when it allows citizens to interact with government without making essential rights dependent on technology they cannot understand, access, or contest.
