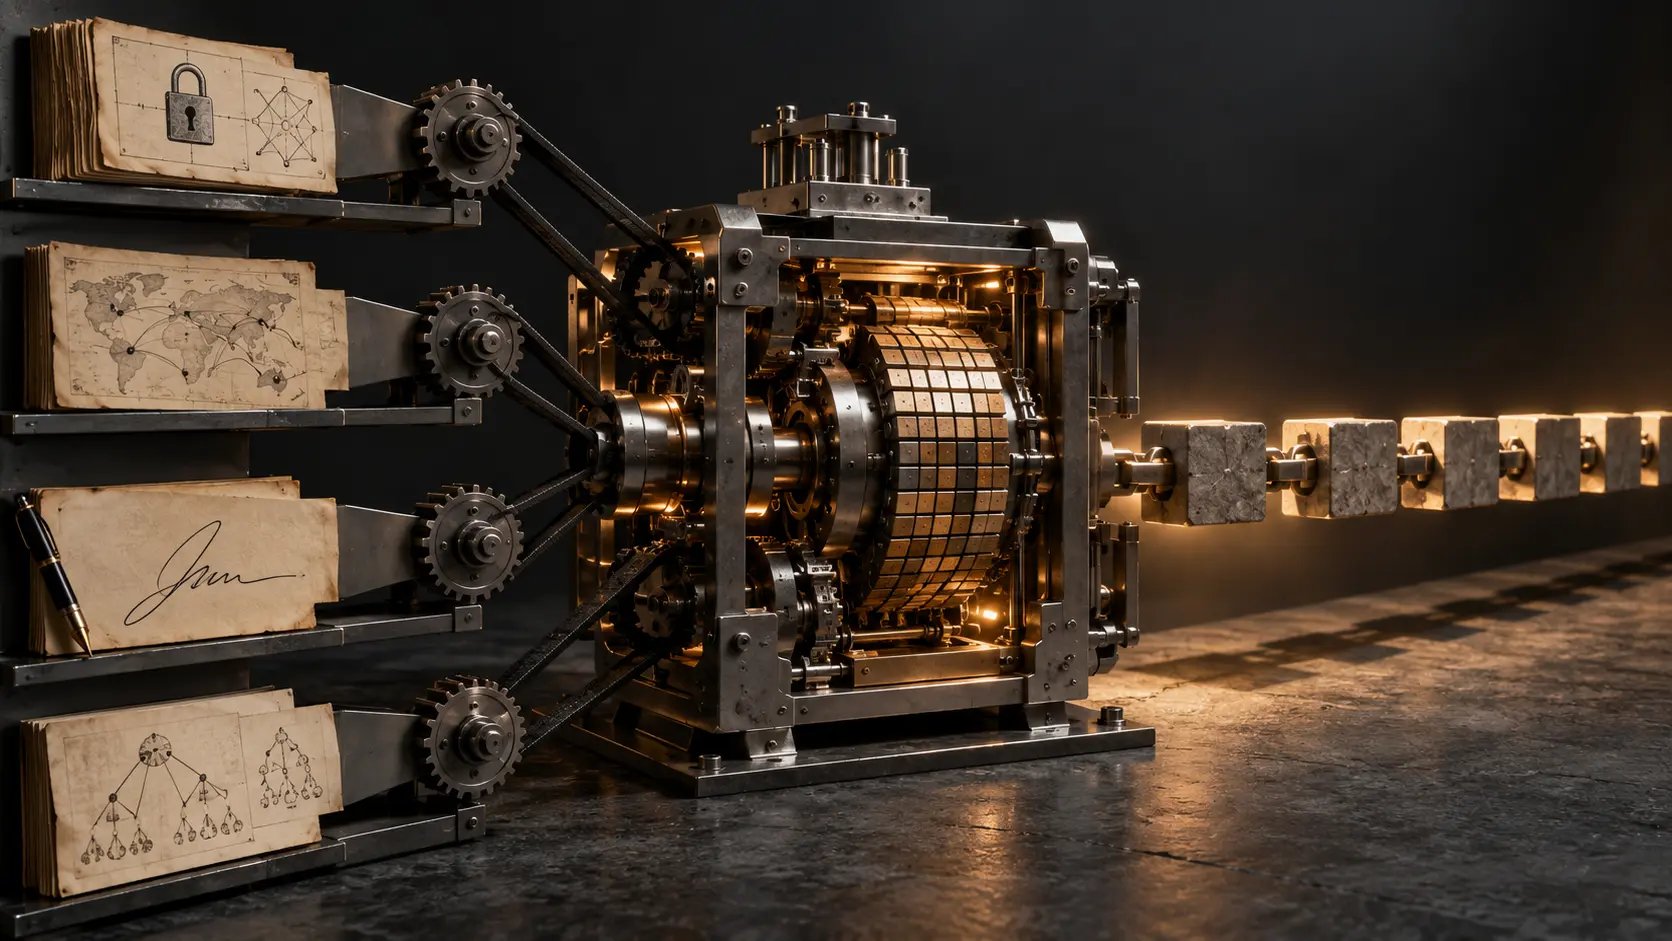
Bitcoin did not appear because someone suddenly invented cryptography, digital signatures, distributed networks, or computational proof. All of those ideas already existed before Bitcoin was introduced. Its originality came from combining established technologies in a way that solved a particular problem: how to maintain a scarce digital asset and a shared transaction history without placing one institution in charge of the system. The innovation was therefore largely architectural. Bitcoin assembled existing pieces so that they reinforced one another and produced properties that none of them provided alone.
This distinction matters because technological breakthroughs are often imagined as completely new inventions appearing from nowhere. In practice, major innovations frequently emerge from combinations. The internet itself was built from earlier work in networking, communication protocols, computing, and packet switching. Smartphones combined processors, wireless communication, touchscreens, cameras, positioning systems, and software platforms that had developed over many years. Bitcoin followed a similar pattern. Its individual components had histories of their own, but their particular arrangement created something different.
Cryptography was one of those foundations. Long before Bitcoin, cryptographers had developed mathematical techniques for protecting information and proving that certain actions had been authorized. Public-key cryptography made it possible for people to use related pairs of keys: one could remain secret while another could be shared publicly. This opened the door to digital signatures, which allow someone to approve a digital message in a way that others can verify without learning the secret key used to create the signature.
For digital money, this is extremely useful. A Bitcoin transaction must provide some evidence that the person attempting to spend particular funds has the authority to do so. Digital signatures provide that evidence. A user can authorize a transaction with a private key, and the network can verify the authorization using cryptographic information available publicly. There is no need for a bank employee to check a handwritten signature or for a central company to maintain a password database for every transaction.
But digital signatures do not create digital money by themselves. They can prove that someone authorized a message, but they cannot determine whether the same funds have already been spent elsewhere. A person could sign two conflicting payment instructions. Both signatures might be perfectly valid. The system would still need a way to decide which payment should be accepted.
Cryptographic hash functions supplied another important piece. A hash function takes digital information and produces a fixed-size result that acts somewhat like a fingerprint of that information. Even a small change in the original data produces a very different result. Hashes can therefore be used to connect pieces of data and make later modifications easy to detect.
The idea of linking records cryptographically also existed before Bitcoin. Researchers had explored methods for timestamping digital documents so that people could demonstrate that information existed in a particular form at a particular time. By connecting records using hashes, it became possible to make alterations to earlier entries visible. Bitcoin adapted this general idea to its transaction history, linking blocks of transactions so that changing an older block would affect the cryptographic relationships with everything built after it.
Even this was not enough. A record can be cryptographically linked and still be controlled by a central administrator. Bitcoin needed a way for independent participants to agree on which version of the record should be accepted when competing versions appeared. That is where proof of work became especially important.
Proof of work also predates Bitcoin. Before it was used for cryptocurrency, related ideas had been proposed as a way to make certain types of unwanted digital activity more expensive. The basic concept is simple: require a computer to perform work that is costly to produce but relatively easy for others to verify. If sending millions of abusive messages required meaningful computational effort for each one, for example, large-scale abuse could become more expensive.
Bitcoin gave proof of work a different role. Miners perform computational work while competing to add new blocks to the transaction history. Producing a valid block requires resources, while checking that the required work was performed is comparatively straightforward. This gives the network a practical way to attach economic cost to the process of extending the ledger.
The significance of proof of work becomes clearer when there is disagreement. In a distributed network, different participants may briefly receive different versions of recent events. Two valid blocks can even appear close together. Bitcoin needs a rule that allows participants to converge on a common history rather than remain permanently divided. Proof of work gives the network an objective basis for comparing competing histories and coordinating around the chain representing the greatest accumulated work under the protocol's rules.
This does not mean proof of work alone creates consensus. Bitcoin's consensus emerges from several components working together. Nodes check whether transactions and blocks satisfy the protocol. Miners compete to extend the transaction history. Economic incentives encourage miners to follow rules that other participants will accept, because producing blocks that everyone rejects would waste resources. Users, businesses, exchanges, and other participants decide which software and rules they recognize. The resulting system is not a single mechanism but a carefully connected set of technical and economic relationships.
Distributed networks were another existing ingredient. Computers had been communicating directly with one another in peer-to-peer systems before Bitcoin. Such networks can distribute information without requiring every message to pass through one central server. They can also remain available even when some individual computers disconnect.
Bitcoin uses this structure to distribute transactions and blocks among participants. A user can broadcast a transaction into the network, nodes can relay it, and miners can include it in a block. Copies of the blockchain can exist on many computers. This reduces dependence on a single server whose failure could stop the entire system.
Yet peer-to-peer networking alone cannot solve the monetary problem either. A network can easily distribute conflicting information. If one computer says Alice paid Bob while another says Alice paid Carol with the same funds, simply copying both messages across thousands of machines does not establish which one should count. Distribution spreads information; it does not automatically create agreement. Bitcoin needed cryptography, transaction rules, proof of work, and incentives to turn a distributed communication network into a system capable of maintaining a common financial history.
Earlier digital-money projects had already explored parts of this territory. Researchers had spent years thinking about electronic cash, privacy, cryptographic ownership, and ways to reduce reliance on conventional payment intermediaries. Some proposed systems depended on a central issuer. Others experimented with distributed approaches or computational scarcity. Bitcoin emerged from this broader history rather than beginning the field from zero.
What Bitcoin did unusually well was connect the pieces around the double-spending problem. Digital information can be reproduced at almost no cost, but money requires scarcity. If one digital unit could be copied and spent repeatedly, recipients could not trust payments. Traditional digital finance solves this by allowing banks and payment systems to maintain authoritative ledgers. Bitcoin sought to achieve the same basic requirement without appointing one institution to decide which transaction history was definitive.
Digital signatures helped answer who was authorized to spend. The transaction ledger recorded what had already been spent. Cryptographic hashes connected the history and exposed tampering. Proof of work made rewriting that history costly and provided a basis for choosing between competing versions. The peer-to-peer network allowed information to propagate without a central server. The issuance and reward system gave miners an economic reason to spend resources securing the network. Each component addressed a different part of the overall problem.
The economic incentives are particularly important because Bitcoin is not only a cryptographic system. It is also a system designed around the behavior of participants who may be motivated by self-interest. Miners incur real costs when performing computational work, so the protocol provides them with potential rewards. Those rewards come from newly issued bitcoin and transaction fees. A miner generally has an incentive to produce blocks that the rest of the network will accept rather than spend resources producing invalid ones.
This combination of cryptography and incentives distinguishes Bitcoin from a system that merely assumes participants will cooperate. It does not require every miner to be generous, trustworthy, or personally committed to the network. Instead, the system attempts to make rule-following economically rational while making certain forms of manipulation expensive. The design recognizes that technical security in an open financial network also depends on incentives.
Bitcoin's supply rules fit into the same architecture. The protocol defines how new bitcoin is issued and places constraints on that issuance. Nodes can independently verify whether a miner has created more bitcoin in a block than the rules permit. This means monetary issuance is connected to the same verification system that checks transactions. The scarcity of BTC is therefore not simply a promise written by an issuing company; it is a rule participants can verify through software.
None of these elements should be treated as magical or infallible. Cryptographic systems can have implementation errors. Software can contain bugs. Users can lose private keys. Mining can become concentrated. Network participants can disagree about software changes. Economic incentives can produce unexpected behavior. Bitcoin's importance does not come from eliminating every possible problem, but from showing that previously separate ideas could be assembled into a functioning decentralized monetary network.
This also explains why identifying a single invention as "the technology behind Bitcoin" can be misleading. Bitcoin is not merely blockchain, proof of work, cryptography, or peer-to-peer networking. Remove digital signatures and ownership authorization breaks down. Remove the shared transaction history and double spending becomes difficult to resolve. Remove a mechanism for establishing consensus and participants can disagree indefinitely. Remove the communication network and the system cannot propagate transactions efficiently. The architecture matters because the components depend on one another.
The blockchain itself is a good example of how focusing on one component can obscure the larger design. A chain of cryptographically linked records is useful, but by itself it does not explain why strangers should agree on one version of that chain. Nor does it explain who is allowed to spend assets or why participants should spend resources securing the history. Bitcoin's achievement came from embedding the chain inside a broader system of verification, consensus, incentives, and decentralized communication.
Understanding this history also changes how innovation is evaluated. An invention does not have to contain entirely new scientific ingredients to be genuinely original. Combining mature technologies in a way that solves an unsolved coordination problem can be a major innovation in its own right. The novelty may lie in recognizing that existing tools can be arranged differently and in designing the rules that allow them to operate together.
Bitcoin was built in precisely that way. Cryptography provided tools for authorization and integrity. Digital signatures made ownership claims verifiable. Hashes helped connect and protect the transaction history. Proof of work introduced a costly mechanism for extending that history and resolving competition between versions. Distributed networking allowed independent computers to participate without relying on one central server. Economic incentives encouraged participants to devote resources to the system.
The result was not merely a collection of old technologies placed side by side. Their interaction created a new architecture for digital scarcity, ownership, and transaction agreement. Bitcoin's originality therefore lies less in inventing every component than in understanding how those components could solve one another's weaknesses. The pieces already existed. The breakthrough was the way they were made to work together.
