Cyberattacks work by exploiting weaknesses in digital systems, human behavior, or the relationships between different technologies. An attacker does not always need to break through a sophisticated security barrier. Sometimes the entry point is an unpatched application, a misconfigured cloud service, a stolen password, or a convincing message that persuades someone to reveal sensitive information. Understanding how do cyberattacks work therefore requires looking at security as a complete system rather than as a single product such as antivirus software.
Every digital environment is made up of many interconnected parts. Personal devices connect to applications, applications depend on databases, employees use accounts to access internal systems, servers communicate across networks, and cloud services exchange information with external providers. Each connection creates useful functionality, but it can also create another opportunity for misuse. A weakness in one component may allow an attacker to reach another component that would otherwise be protected.
Software vulnerabilities are one of the most familiar sources of risk. Modern applications contain millions of lines of code, and programming mistakes are inevitable. Some bugs affect only performance or reliability, but others can allow an attacker to bypass security controls, access information, or make a system perform actions it was never intended to perform. When a serious vulnerability is discovered, software developers usually release a patch that corrects the problem.
The danger grows when patches are not installed promptly. Organizations often operate large numbers of servers, computers, mobile devices, industrial systems, and business applications. Keeping all of them updated can be difficult, especially when older software depends on specific versions or when administrators fear that an update could interrupt operations. Attackers can take advantage of this delay by targeting known vulnerabilities that already have fixes available.
Not every weakness is caused by faulty software. Configuration errors can create equally serious problems. A cloud storage system may accidentally be made publicly accessible, a database may be exposed to the internet, or an administrator account may be granted more privileges than necessary. The underlying software may be functioning correctly, but the way it has been configured creates an opening.
Credentials are another major target. Usernames, passwords, security tokens, and other authentication information are valuable because they can allow an attacker to enter a system without exploiting software at all. Credentials can be stolen through phishing, malware, data breaches, password reuse, or poorly protected databases. Once attackers obtain a valid account, their activity may initially look similar to legitimate use.
Password reuse makes this especially dangerous. If someone uses the same password across several services and one of those services is breached, attackers may try the exposed credentials elsewhere. This is one reason unique passwords and multi-factor authentication are important. Multi-factor authentication adds another verification step, making a stolen password less useful by itself.
Social engineering attacks focus on people rather than software. The attacker tries to persuade someone to reveal information, open a malicious file, approve a login, transfer money, or perform another action that weakens security. Phishing emails are a common example, but social engineering can also happen through text messages, phone calls, social media, or impersonation.
These attacks are effective because they exploit normal human behavior. Employees are expected to respond to colleagues, open business documents, approve requests, and solve problems quickly. An attacker may imitate a manager, supplier, bank, technical support worker, or trusted service in order to make a fraudulent request seem legitimate. The technical component may be simple, but the manipulation can be carefully planned.
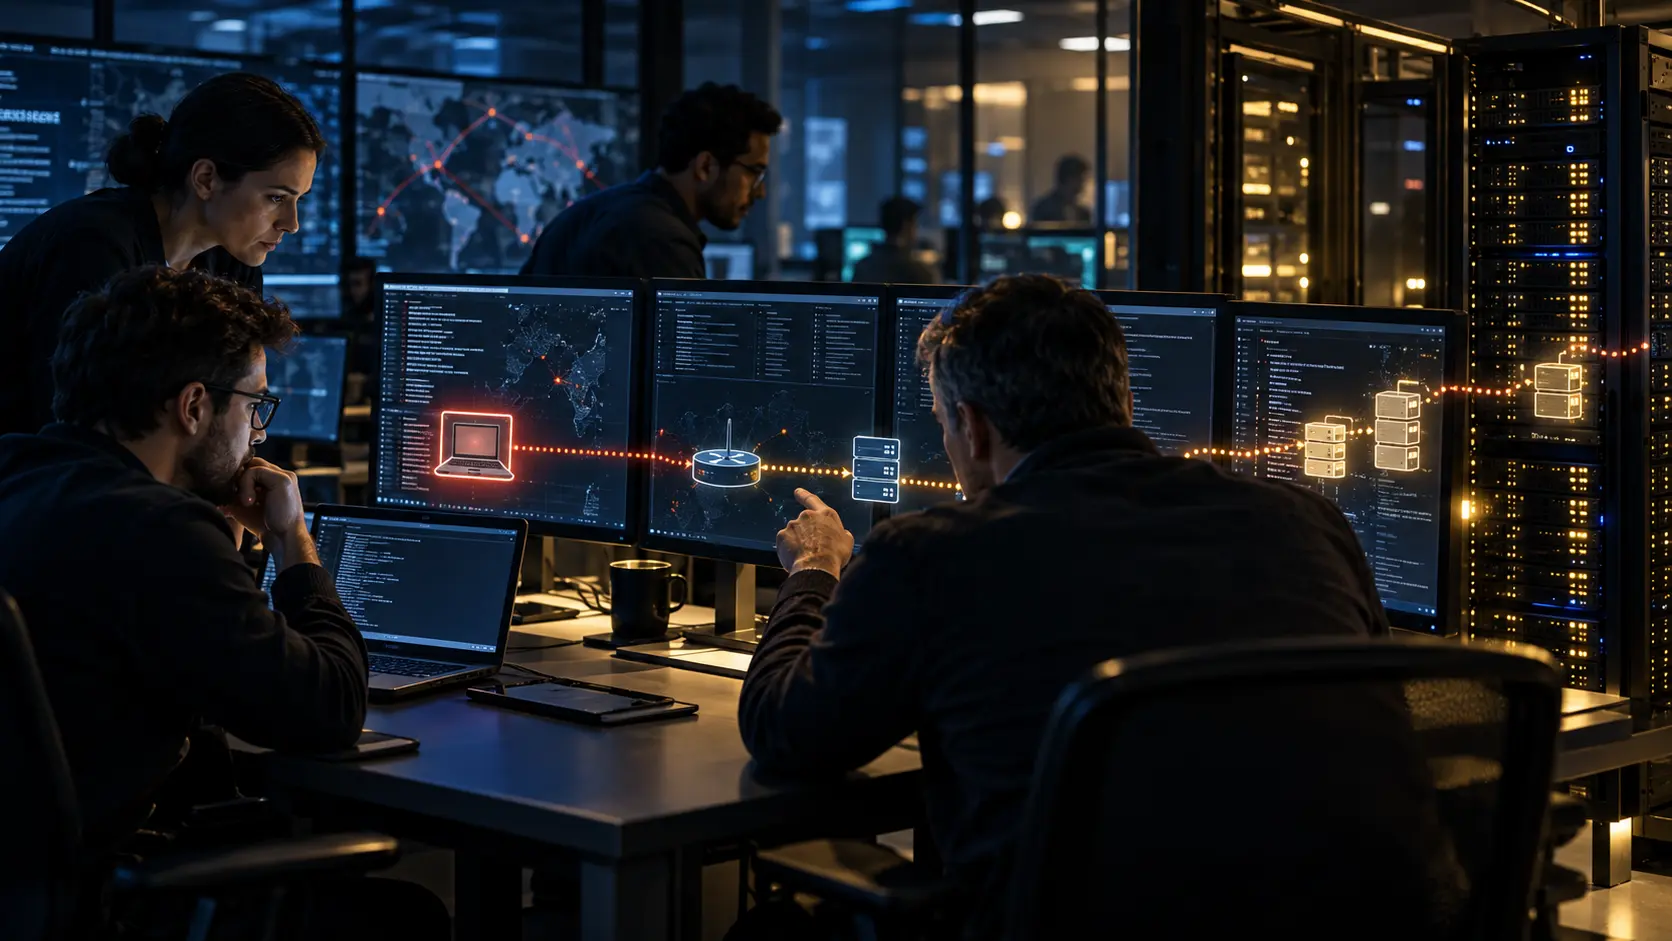
Some attacks combine several weaknesses. An attacker might first steal an employee's password through phishing, use that account to enter a cloud service, discover an overly permissive administrative role, and then access systems that the original employee did not normally use. The initial entry point may be small, while the eventual impact can be much larger.
This process is often described as moving through stages. An attacker gains initial access, looks for valuable systems, attempts to increase privileges, moves between connected resources, and tries to reach data or operations worth stealing or disrupting. The exact sequence varies, but the important point is that the first compromised device is not always the final target.
Privileges matter because digital systems usually give different users different levels of authority. An ordinary employee may be able to read documents but not change security settings, while an administrator can create accounts, install software, or access sensitive databases. Attackers therefore often try to obtain more powerful credentials after entering a network.
This is known as privilege escalation. It can happen through software vulnerabilities, poor permission settings, stolen administrator passwords, or exposed authentication tokens. Once an attacker gains elevated access, it becomes much easier to disable security controls, create additional accounts, or reach restricted systems.
Networks can also provide pathways between systems. A company may secure its public website carefully while leaving internal connections more open because they were designed for trusted employees. If an attacker compromises one internal machine, those trusted relationships can become useful for moving deeper into the environment.
This is why modern security strategies increasingly avoid assuming that anything inside a network is automatically safe. Access can be continuously checked according to identity, device condition, location, and the sensitivity of the requested resource. The broader principle is that trust should be limited and verified rather than granted simply because a device is already connected.
Malware is another common tool in cyberattacks. Malware is software designed to perform unwanted actions, such as stealing information, spying on users, damaging files, or giving an attacker remote control. Some malware spreads automatically, while other forms depend on a victim opening a file or installing a program.
Ransomware is a particularly disruptive form of attack. It can encrypt files or interfere with systems so that an organization loses access to critical information. Attackers may then demand payment. In some cases, they also steal data before disrupting operations and threaten to release it publicly.
The damage from ransomware can extend far beyond computers. If hospitals, factories, logistics companies, or public agencies depend on affected systems, digital disruption can interfere with physical operations. Employees may lose access to schedules, records, inventory systems, or communication tools even when the underlying machinery itself is undamaged.
Web applications create another large attack surface. Online services receive data from users continuously, and that data must be handled carefully. Weak input validation, insecure authentication, or poorly designed access controls can sometimes allow unauthorized users to view or modify information. Because web applications are exposed to the internet, attackers can often probe them remotely.
Application programming interfaces, or APIs, are especially important in modern systems. APIs allow applications to exchange information automatically. Mobile apps, payment systems, cloud platforms, and business services depend heavily on them. If an API does not properly verify who is making a request or what that person is allowed to access, sensitive data may be exposed.
Cloud computing changes the security environment without removing the basic risks. Cloud providers protect much of the underlying physical infrastructure, but customers are still responsible for configuring accounts, permissions, applications, and data correctly. A secure cloud platform can still be used insecurely if access controls are weak or credentials are exposed.
Supply chains create another layer of risk. Organizations rarely build every piece of technology themselves. They depend on software vendors, cloud providers, contractors, libraries, hardware suppliers, and external service companies. If one trusted supplier is compromised, attackers may be able to reach many customers through that relationship.
This is especially serious when a widely used software component contains a vulnerability or malicious modification. A single problem can affect thousands of organizations at once. The interconnected nature of modern technology means that security depends partly on companies and systems outside an organization's direct control.
Cyberattacks can also target availability rather than secrecy. A distributed denial-of-service attack attempts to overwhelm a website or online service with more traffic than it can handle. The goal may not be to steal information but simply to make the service unavailable to legitimate users.
Attackers can generate large amounts of traffic using networks of compromised devices known as botnets. These devices may include computers, servers, routers, cameras, or other internet-connected equipment. Because the traffic comes from many sources, blocking it can be more difficult than stopping requests from a single machine.
Data theft has different objectives. Attackers may seek customer records, financial information, intellectual property, passwords, business plans, or government data. Sometimes the stolen information is sold, used for fraud, or employed in further attacks. In other cases, espionage rather than immediate financial gain may be the objective.
Detection can be difficult because sophisticated attackers often try to appear normal. Instead of causing obvious damage immediately, they may move slowly, use legitimate administrative tools, and access systems during ordinary business hours. Security teams therefore analyze patterns of behavior as well as obvious malware or known attack signatures.
Logs are important for this purpose. Servers, applications, network devices, and identity systems record information about activity. Security teams can examine these records for unusual login locations, unexpected access to sensitive data, or sudden changes in administrative privileges.
However, collecting logs is only useful if organizations can interpret them. Large environments generate enormous volumes of security data. Automated monitoring systems can help identify suspicious patterns, but human judgment remains important when deciding whether an unusual event is harmless or part of an attack.
Security therefore depends on layers of protection. Antivirus software can detect some malicious programs, but it cannot stop every type of compromise. Firewalls can block certain network connections, but they cannot prevent an employee from voluntarily giving credentials to a convincing impersonator. Strong passwords help protect accounts, but they do not fix vulnerable software.
A more complete approach protects devices, applications, networks, identities, and data at the same time. It includes software updates, access controls, encryption, backups, monitoring, employee training, incident response plans, and limits on unnecessary privileges. The goal is not to assume that every attack can be prevented, but to make attacks harder, detect them earlier, and reduce the damage if they succeed.
Backups are particularly important because some attacks are designed to destroy or encrypt information. A reliable backup can allow an organization to recover without depending entirely on the compromised systems. However, backups must be protected as carefully as production data, because attackers may try to delete or encrypt them as well.
Segmentation can also limit damage. Instead of allowing every device to communicate freely with every other system, organizations can separate networks and services into smaller zones. If one area is compromised, the attacker may have difficulty reaching more sensitive systems.
The growing number of connected devices makes this increasingly important. Smart cameras, industrial controllers, medical devices, home appliances, vehicles, and sensors all communicate through digital networks. Many of these devices have different security capabilities and may remain in use for years.
Greater interconnection increases the consequences of failure because digital systems increasingly control physical and economic processes. A compromised office computer may expose documents, but an attack on industrial systems can interrupt production. An attack on financial infrastructure can delay payments, while an incident affecting communications networks can disrupt services across large areas.
This does not mean that every connected system is dangerously fragile. Interconnection also makes it possible to build redundancy, remote monitoring, and faster recovery. The challenge is that dependence spreads risk. When many organizations rely on the same cloud provider, software library, authentication service, or network infrastructure, one failure can have unusually broad consequences.
Cybersecurity is therefore partly an architectural problem. Systems should be designed so that one mistake does not automatically give an attacker unlimited access. Critical functions can be separated, permissions minimized, sensitive data encrypted, and multiple controls placed between an initial breach and the most valuable assets.
Human behavior remains part of that architecture. Employees need clear procedures for verifying unusual requests, reporting suspicious messages, and handling sensitive information. Security rules that are too complicated can sometimes encourage people to work around them, so good security also requires systems that are practical to use.
No organization can remove every vulnerability. Software changes, employees make mistakes, equipment ages, and new attack techniques appear. Effective cybersecurity is therefore an ongoing process of identifying weaknesses, reducing exposure, monitoring activity, and responding quickly when something goes wrong.
Understanding how do cyberattacks work makes clear why there is rarely a single point of failure or a single defensive solution. Attacks can exploit code, configurations, credentials, human trust, supply chains, and connections between systems. The more digital infrastructure becomes integrated into business, government, finance, industry, and daily life, the more important it becomes to protect the entire environment rather than focusing on one device or one security product.
Modern cybersecurity is ultimately about managing interconnected risk. A strong password matters, but so do secure applications, limited permissions, reliable backups, protected networks, careful configuration, and informed users. Cyberattacks succeed when weaknesses align. Good security reduces the chance that one weakness can become a path through the entire digital system.