AI agents are artificial intelligence systems designed not only to produce answers but also to pursue goals through a sequence of actions. Instead of waiting for a person to specify every step, an agent can interpret an objective, decide what needs to happen, use available tools, evaluate the results, and continue working until it reaches an acceptable outcome or encounters a limit. This ability to move from responding to acting is one of the most important changes in the development of modern artificial intelligence.
The distinction becomes clearer when AI agents are compared with conventional chatbots. A traditional chatbot usually follows a simple interaction pattern: the user sends a message, the system generates a response, and the exchange ends until another message arrives. Even sophisticated language models can operate this way. They may explain difficult concepts, write code, summarize documents, or answer questions, but the user remains responsible for deciding what should happen next. An AI agent can take on more of that responsibility. Given a goal such as preparing a market report, it might determine what information is needed, search approved data sources, organize the findings, perform calculations, create a document, check its own work, and revise sections that appear incomplete.
This does not mean that an AI agent possesses human-like intentions or independent desires. Its apparent autonomy comes from the way the system is designed. The agent receives an objective, operates within a set of instructions and permissions, observes information from its environment, and chooses actions that it estimates will help accomplish the objective. The more tools and decision-making freedom it receives, the more complex its behavior can become.
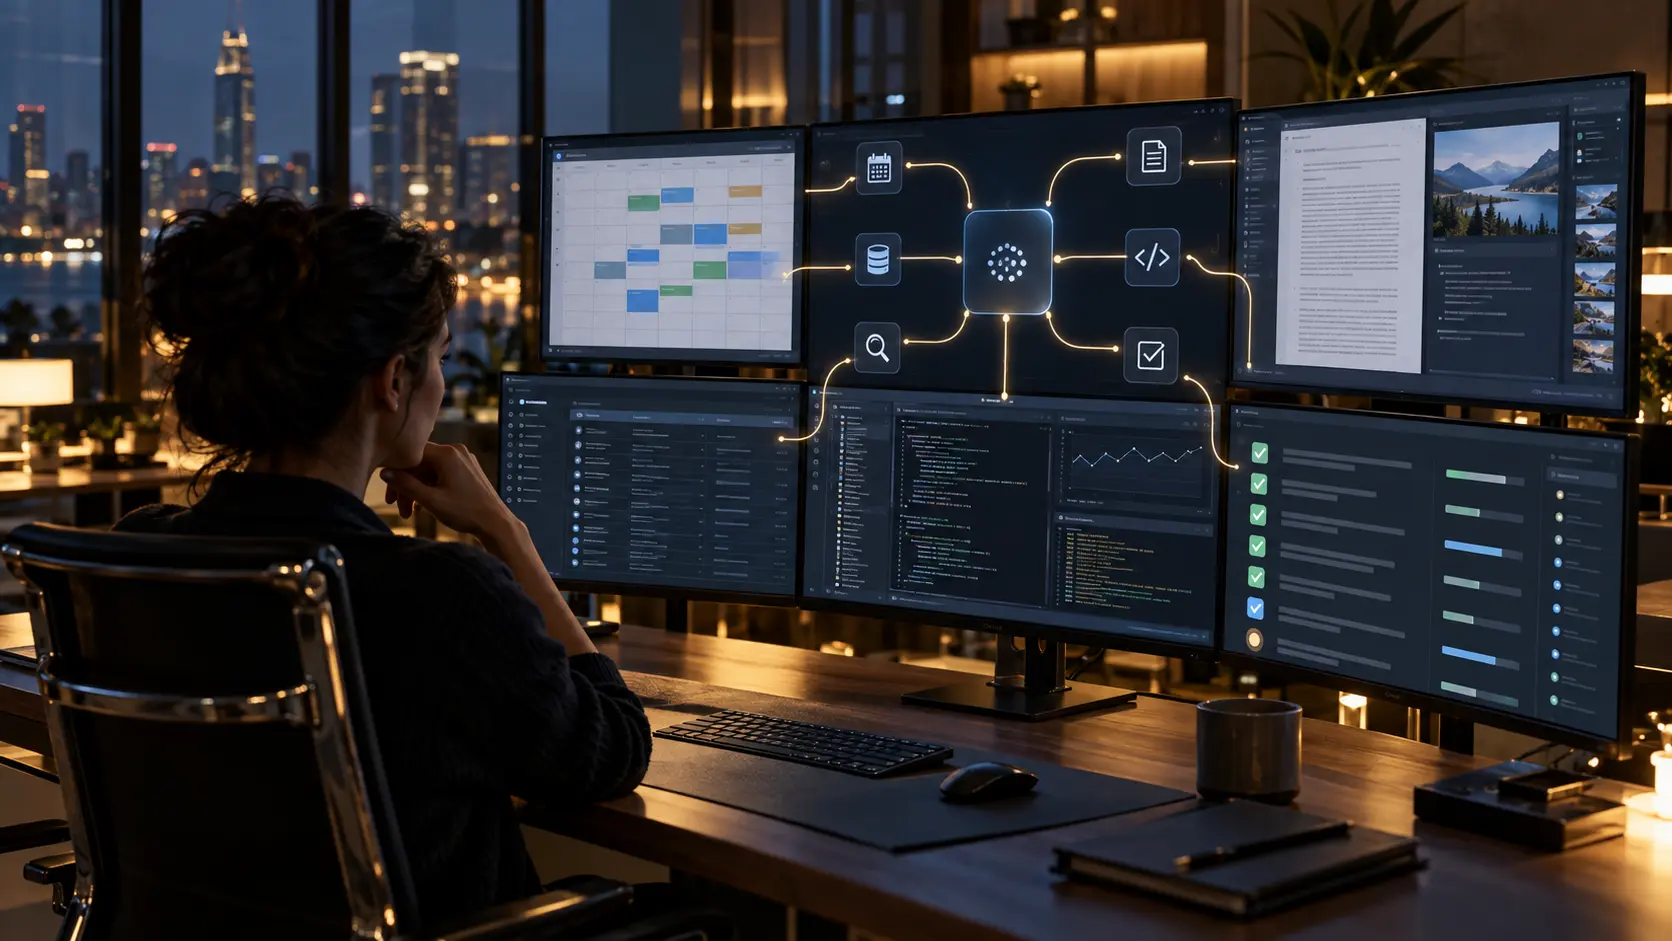
Most modern AI agents combine several components. A language model often serves as the reasoning and communication engine, allowing the system to interpret instructions, analyze information, and decide what to do next. The agent may also have access to memory, external tools, databases, software applications, web services, or specialized models. A control system coordinates these elements, tracks progress, and determines when the task is finished or when human intervention is required.
A typical agent operates through a repeating cycle. It first receives a goal and gathers relevant information. It then develops a plan or selects an immediate action. After acting, it observes the result and uses that new information to decide what should happen next. This process can continue through many steps. For example, an agent asked to organize a business trip might check calendars, compare travel options, identify suitable accommodations, prepare an itinerary, and request approval before making reservations. Each action changes the information available to the agent and influences the next decision.
Tool use is especially important because it allows AI agents to move beyond text generation. A language model by itself can describe how to perform a task, but an agent connected to tools may be able to perform parts of that task directly. Depending on its permissions, it could search a database, run computer code, update a spreadsheet, create a support ticket, retrieve information from business software, or send a message. This connection between reasoning and action is what makes agent-based systems potentially useful for complex workflows.
Memory can also make agents more capable. Short-term memory helps an agent keep track of what has already happened during a task, while longer-term memory can preserve useful information across interactions. An agent assisting with a long-running project, for instance, may need to remember previous decisions, preferred formats, unresolved problems, and completed work. However, memory also introduces concerns about accuracy, privacy, and outdated information. A stored fact can be useful only if it remains relevant and trustworthy.
Another important feature is planning. Simple agents may choose one action at a time, while more advanced systems can break a larger objective into smaller tasks and determine an order for completing them. A software development agent might inspect existing code, identify the files that require changes, write modifications, run tests, analyze failures, and try again. This resembles a workflow carried out by a human, although the quality of the planning depends heavily on the model, the available tools, and the safeguards built around it.
The practical applications of AI agents are expanding across many fields. In customer service, agents can gather account information, diagnose common problems, update records, and escalate unusual cases to human staff. In software engineering, they can help inspect code, generate tests, investigate errors, and automate routine development tasks. In business operations, they may assist with reporting, document processing, data entry, procurement, scheduling, or internal research. Agents can also support scientific work by organizing information, analyzing datasets, or coordinating computational tasks.
Personal productivity is another area where agents may become increasingly visible. Instead of asking an assistant to explain how to organize a project, a user could assign the project itself within defined limits. The agent might review files, extract deadlines, create a schedule, draft communications, and keep track of unfinished work. This changes the relationship between people and AI. The system is no longer used only as a source of information or generated content; it becomes a participant in the workflow.
Greater autonomy, however, creates greater risk. A chatbot that gives an incorrect answer may mislead a user, but an agent that acts on an incorrect conclusion can create additional consequences. It might modify the wrong file, send an inaccurate message, select an unsuitable option, or trigger a process that is difficult to reverse. Errors can also accumulate across multiple steps. If an early assumption is wrong, later decisions based on that assumption may move the agent farther from the intended result.
For this reason, reliable AI agents require more than powerful language models. They need carefully designed permissions, monitoring systems, validation mechanisms, and clear boundaries. High-impact actions may require human approval, while lower-risk tasks can be performed automatically. An organization might allow an agent to draft an email but require a person to approve it before sending, or permit it to analyze financial records without allowing it to transfer money. These restrictions reduce autonomy, but they can make the system substantially safer.
Security is another major challenge. Because agents can interact with external systems, they may be exposed to malicious or misleading information. An agent reading web pages, emails, or documents could encounter instructions designed to manipulate its behavior. If it has broad access to sensitive tools, a successful attack could have more serious consequences than it would for a system that only generates text. Strong authentication, limited permissions, trusted data sources, and careful separation between instructions and untrusted content are therefore essential parts of agent design.
AI agents also face technical limitations that prevent them from operating with complete reliability. Language models can misunderstand instructions, invent information, select inappropriate tools, or fail to recognize that a plan is not working. Long tasks create additional difficulties because the agent must preserve context, track progress, avoid repeating work, and recover from unexpected results. Real-world environments are often messy, and tools may return incomplete data, change their interfaces, or behave unpredictably.
Evaluating an agent is harder than evaluating a system that produces a single answer. Success may depend on whether the agent completed the correct task, used appropriate methods, avoided unnecessary actions, respected permissions, handled exceptions, and produced a result that can be verified. An agent that reaches the right outcome through unsafe or unreliable behavior may still be unsuitable for practical use. This is why agent evaluation increasingly focuses not only on final results but also on the quality of the process used to reach them.
Human supervision remains important, especially when decisions involve money, safety, legal obligations, personal data, or other significant consequences. The goal of many agent systems is not necessarily to eliminate people from a process. Instead, autonomy can be applied selectively, allowing machines to handle repetitive or well-defined steps while humans retain authority over ambiguous, sensitive, or irreversible decisions. The appropriate balance depends on the task and the cost of an error.
The development of AI agents also raises broader questions about responsibility. When an autonomous system performs an unwanted action, responsibility cannot simply be assigned to the machine. Developers, organizations, tool providers, and users may all influence how the system was designed, deployed, and supervised. Clear records of what an agent did and why can help people investigate mistakes, improve systems, and establish accountability.
As AI agents improve, the most important change may be the shift from software that waits for detailed commands to software that can pursue broader objectives. Traditional programs generally execute procedures specified in advance, while agents can make flexible decisions within the boundaries they are given. This flexibility makes them powerful, but it also makes their behavior less predictable. The challenge is therefore not simply to make agents more autonomous, but to make their autonomy dependable, understandable, and appropriately limited.
AI agents represent an important stage in the evolution of artificial intelligence because they connect reasoning with action. Their value comes from their ability to manage multi-step tasks, use tools, adapt to new information, and reduce the amount of human direction required for routine work. At the same time, every increase in autonomy raises the importance of security, verification, oversight, and responsible design. The future of AI agents will depend not only on how much machines can do on their own, but also on how effectively people can decide what they should be allowed to do.